
SCIMAPI
Provision, update and deprovision users and groups through SCIM 2.0 endpoints, across HR systems and directories, including ones that don't support SCIM themselves.


One request. Every HRIS.
Swap the connection_id and the same code reads employees as SCIM users from Okta, Workday, BambooHR or any of 893 HRIS integrations, in one normalized shape. Every call is live against the source API.
curl --get \
  'https://api.unified.to/scim/{connection_id}/users' \
  --data 'count=1' \
--header "authorization: bearer $UNIFIED_API_KEY"[
{
"id": "5eb3081053162e8b59189272",
"schemas": ["urn:ietf:params:scim:schemas:core:2.0:User"],
"userName": "daniel.kim@foobar.com",
"name": { "givenName": "Daniel", "familyName": "Kim" },
"displayName": "Daniel Kim",
"title": "Product Designer",
"active": true,
"emails": [
{
"value": "daniel.kim@foobar.com",
"type": "work",
"primary": true
}
]
}
]No credit card required. Get your API key, connect real accounts, and make live calls like this one in minutes.
The modern Unified API+MCP platform, built differently
Real-time, pass-through
Every request hits the source API live. No caching or sync jobs: reads and writes go to the source API, and native and virtual webhooks report changes on supported integrations.
No customer records at rest
No customer records at rest; connection credentials and operational metadata are encrypted at rest. Each workspace runs in one region: US on every plan, EU or AU on Pro and Scale.
Common objects across every category
Unified objects, endpoints, scopes and errors across every category, plus raw payloads when you need vendor-specific fields.
Custom fields & objects
Read and write custom fields through the Metadata API; reach custom objects through raw fields and the Passthrough API.
AI-ready integrations
Built for AI products: Unified MCP gives LLMs scoped access to integration tools, with options to limit permissions and hide sensitive fields.
Predictable pricing, no lock-in
Usage-based pricing that scales with API volume, not with the number of customers you connect. Own your credentials and export them anytime; tokens issued to your own OAuth app keep refreshing after you leave.
Get integrations from backlog to production in days
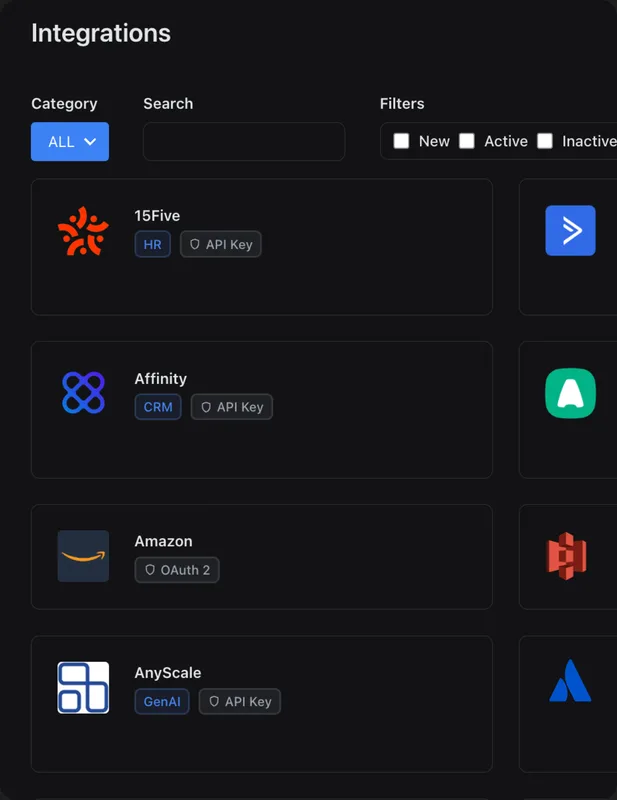
1. Activate integrations
Activate HR & Directory integrations in your workspace. SCIM support comes with them.
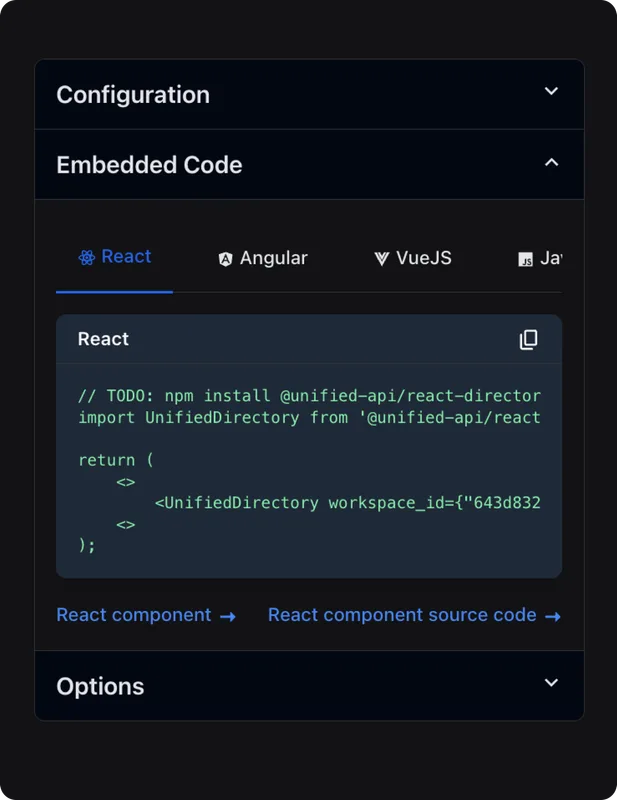
2. Launch integrations
Point your SCIM client at Unified.to's SCIM endpoints, one per connection.
3. Authorize integrations
Authorize customer accounts with the embedded authorization component.
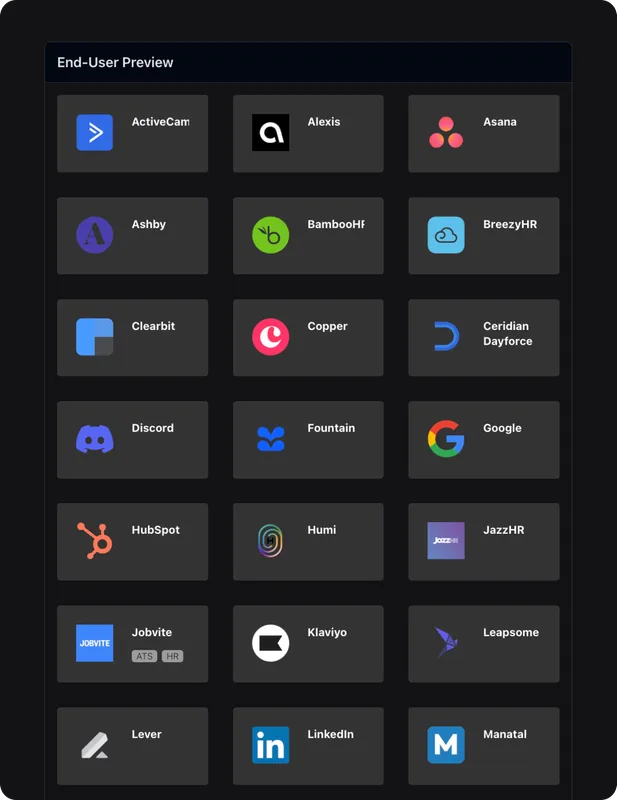
Authorization handled for you
A pre-built authorization component and API handle each vendor's sign-in, so your code works with a connection ID.
See documentation
Business Login
Sign users in with the software their company already runs on. Redirect them to one Unified URL and get back their verified email and name. No OAuth flows to build, no tokens to store.
Built on OpenID Connect (OIDC), OAuth2, and SAML specifications.
Unified supports 318+ sign-in integrations.
Trusted by developers and product teams worldwide
Fresh data to fuel countless use cases
Power AI copilots, insights, predictive analysis, and automation with a modern integration infrastructure that scales alongside you.
Provision Users
Create the user when a new hire is added, and update the profile when the role changes, on integrations that write employees.
Deprovision Users
Delete or deactivate the user when access should end, on integrations that support it.
Sync Groups
Sync groups and memberships to manage access consistently.
Update Profiles
Sync user attributes (name, email, role, department) via SCIM updates.
Why our customers choose us
Integrate.Faster.